
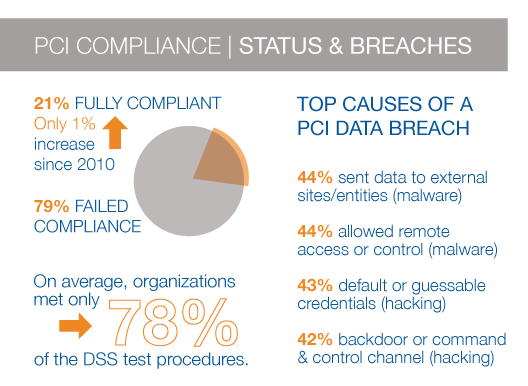
Only 21 percent of organizations were found to be fully PCI compliant during their first assessment of attestation in the Verizon 2011 Payment Card Industry Compliance Report, showing only a 1 percent increase since their 2010 report (statistics based on QSA assessments). Translating to a 79 percent fail percentage, the organizations, on average, only met 78 percent of the test procedures defined in the DSS (Data Security Standards).
Only 21 percent of organizations were found to be fully PCI compliant during their first assessment of attestation in the Verizon 2011 Payment Card Industry Compliance Report, showing only a 1 percent increase since their 2010 report (statistics based on QSA assessments). Translating to a 79 percent fail percentage, the organizations, on average, only met 78 percent of the test procedures defined in the DSS (Data Security Standards).

PCI Compliance Status Breaches
Challenges to Meeting Compliance
The report lists a number challenges that serve as barriers to meeting full PCI compliance and the full set of requirements. Those challenges include:
| Trained personnel | Fully staffed and expert IT departments can be difficult to find and maintain for ongoing compliance. |
| Corporate Will | This refers to the inability of management or directors to recognize the importance of compliance – compliance is “considered to be a drag on the economy by most businesses rather than an assumed part of the risk of doing business.”With this type of attitude, resources are often not allocated to meet compliance by implementing proper controls, policies and procedures. |
| Complexity | PCI requirements are specific and lengthy – the Verizon report claims PCI has well over 200 requirements (while the 12 requirements are notorious, each one has multiple listed sub-requirements).The time and resources needed to address each requirement can be extensive. |
What were the most difficult requirements to achieve?
Only 37 percent of organizations met the PCI requirement #11 – regularly test security systems and processes, and 39 percent were able to maintain a policy that addresses information security, requirement #12.
The most challenging sub-requirement, according to the report, was under #10 – tracking and monitoring. #10.5.5 requires organizations to use file-integrity monitoring (FIM) or change detection software on logs to ensure that existing log data cannot be changed without generating alerts.
The two requirements that were achieved by most organizations were #7 – restrict access to data by business need-to-know and #4 – encrypt transmission of cardholder data and sensitive information across public networks.
Another approach to meeting PCI compliance includes reducing scope by meeting certain milestones and thus reducing potential risk to cardholder data. Eighty-eight of organizations met goal #1 – remove sensitive authentication data and limit data retention. Stored sensitive data can be a liability to any organization and decrease their ability to meet compliance requirements.
What are the top causes of a PCI breach?
The report also details the top “threat actions,” meaning the cause or action that contributed to PCI breach incidents. The top five are as follows:
- 44% sent data to external sites/entities (malware)
- 44% allowed remote access or control (malware)
- 43% was due to the exploitation of default or guessable credentials (hacking)
- 42% was due to the exploitation of backdoor or command and control channel (hacking)
- 36% was a result of physical tampering (physical skimmers for the intent of fraud)
While no data center or PCI compliant hosting provider can make an individual merchant PCI compliant, they can help your organization by having PCI compliant controls already in place when it comes to certain technical requirements. Remember, due diligence is always required when you partner with a PCI hosting vendor – check their PCI audit report to determine the full scope and understanding of their compliance; don’t just take their word for it.
References:
Verizon 2011 Payment Card Industry Compliance Report (PDF)